Understanding the eMudhra Key Compromise
Understand the eMudhra key compromise, why weak CA private keys put HTTPS trust at risk, how vendors responded, and what developers should do.
Understand the eMudhra key compromise, why weak CA private keys put HTTPS trust at risk, how vendors responded, and what developers should do.
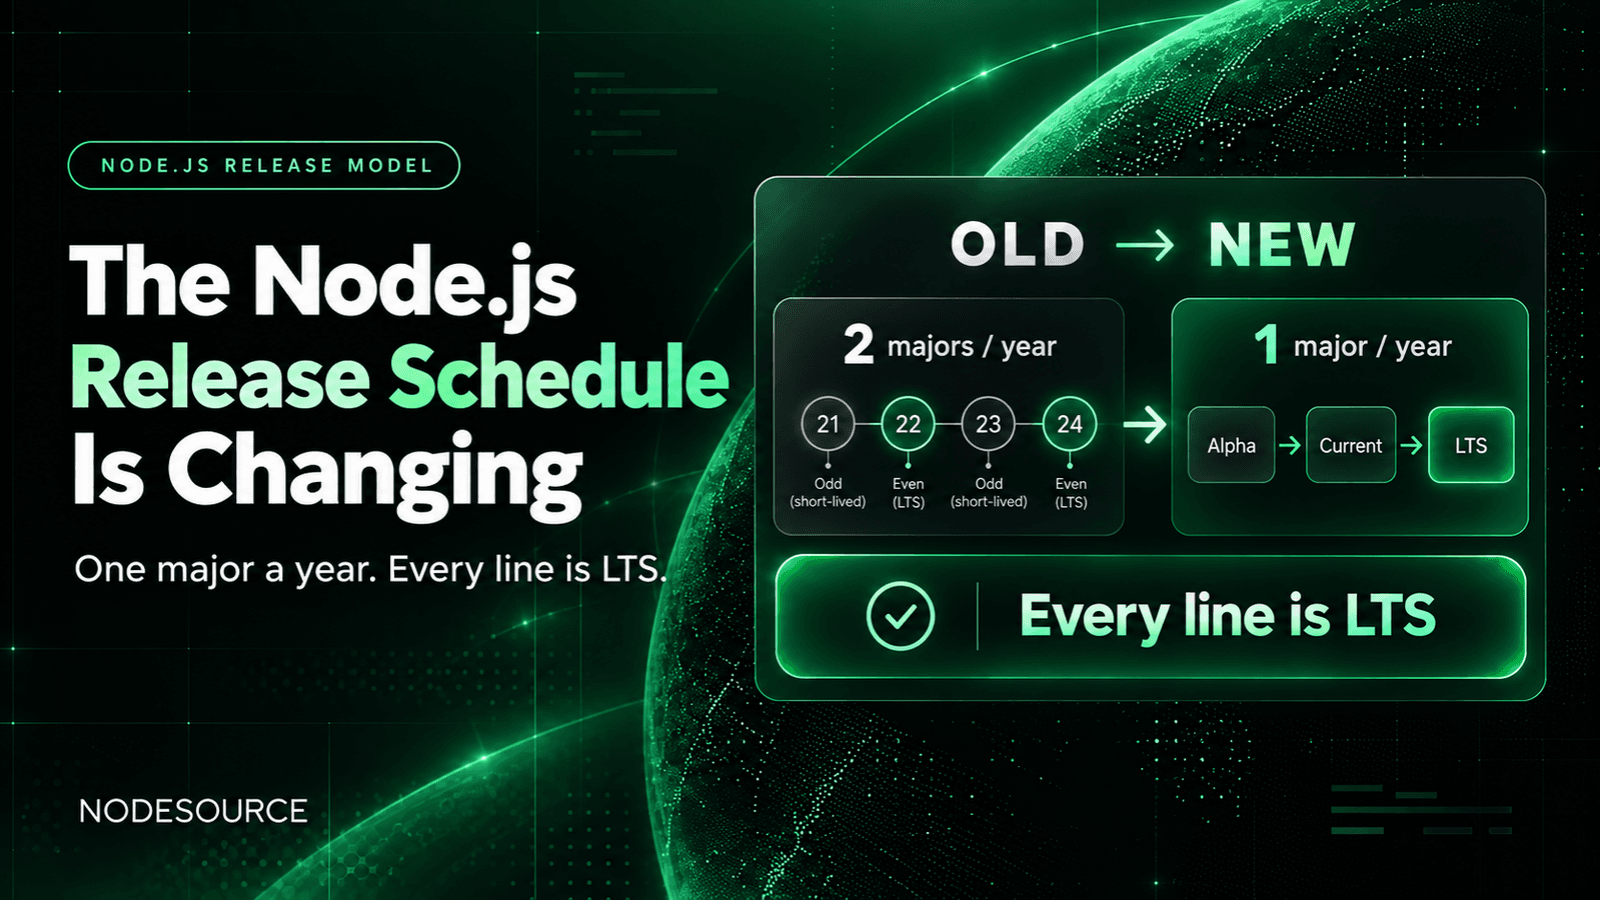
Node.js is moving to one major release per year, with every major headed for LTS and a new Alpha phase. Learn what’s changing and why it matters.
GitHub Actions has removed Node.js 20, and Vercel is ending support. Learn what Node.js 20 EOL means, what’s changing, and how to prepare your projects.
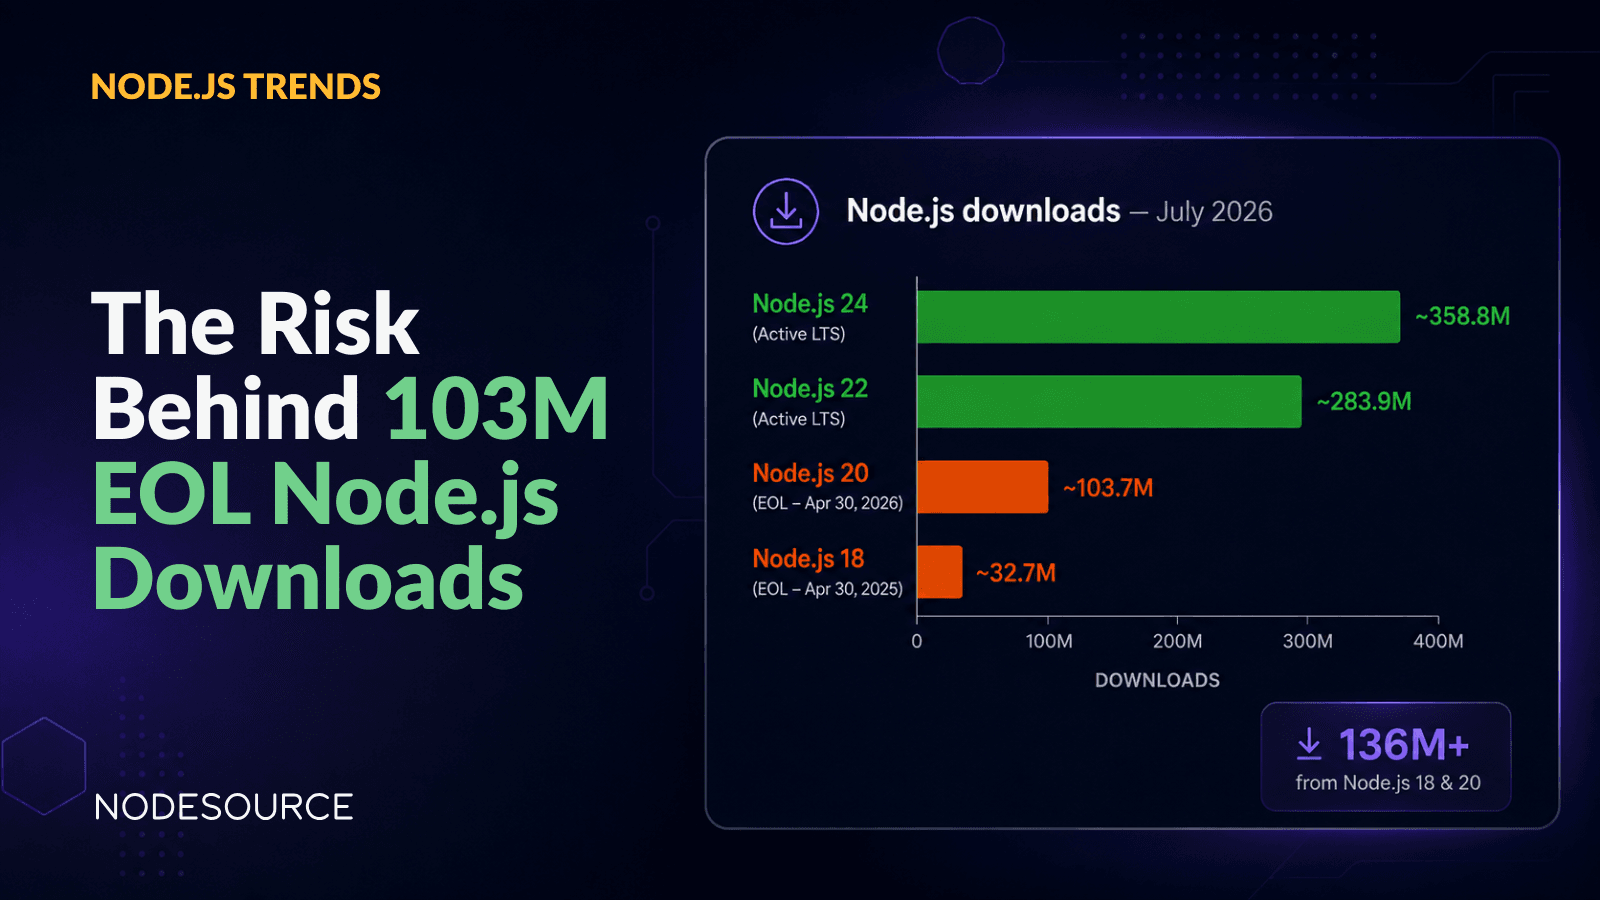
103M Node.js 20 downloads in July 2026 show EOL adoption is still widespread. Explore why teams stay on unsupported versions and the risks involved.
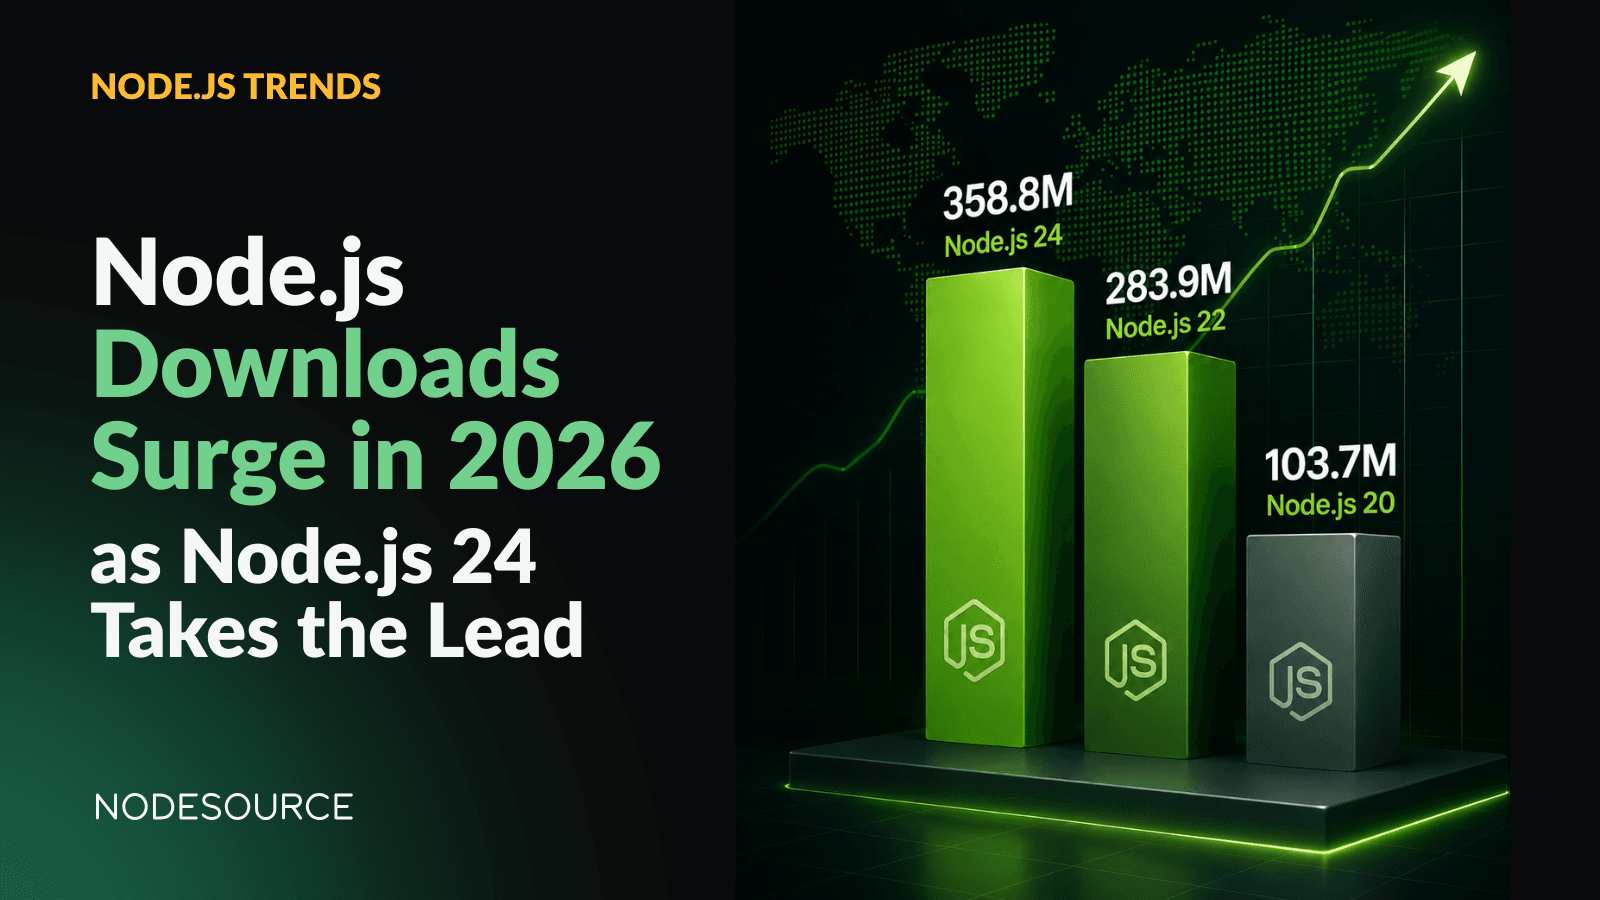
Official Node.js download data shows 2026 has already surpassed 2025 totals, while Node.js 24 leads for the first time. See what the data means for LTS adoption, EOL risk, and modernization.
A HeroDevs analysis found more than 136M downloads of EOL Node.js 18 and 20 in July 2026. Learn why unsupported runtimes remain embedded in active builds.
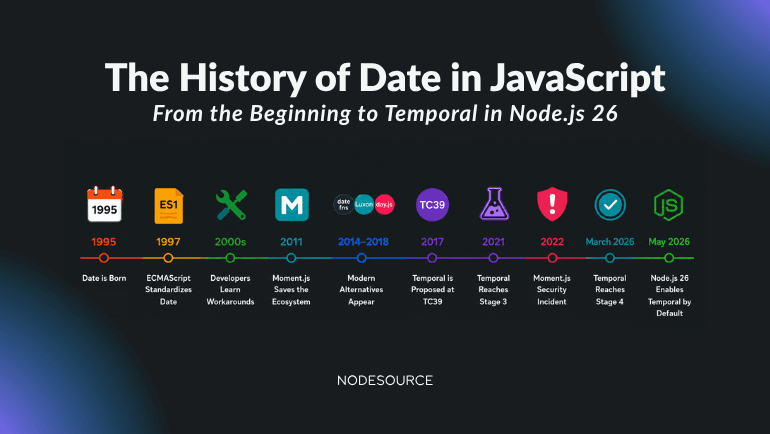
Discover the 31-year journey from JavaScript’s flawed `Date` API to Temporal in ECMAScript 2026 and Node.js 26. Learn how Temporal fixes time zones, parsing, immutability, and modern date handling in JavaScript.
Node.js v26 is now available. Here’s what actually changed: Temporal enabled by default, V8 14.6, Undici 8, and key deprecations.
Anthropic leaked Claude Code via source maps. A Bun bug, missing .npmignore, and weak release checks exposed 500k+ lines of code.
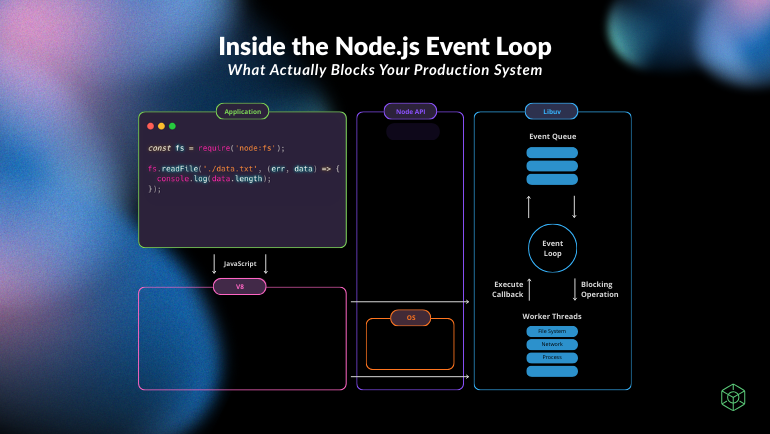
A deep technical breakdown of the Node.js Event Loop, libuv, thread pool behavior, and the real causes of production latency and blocking.
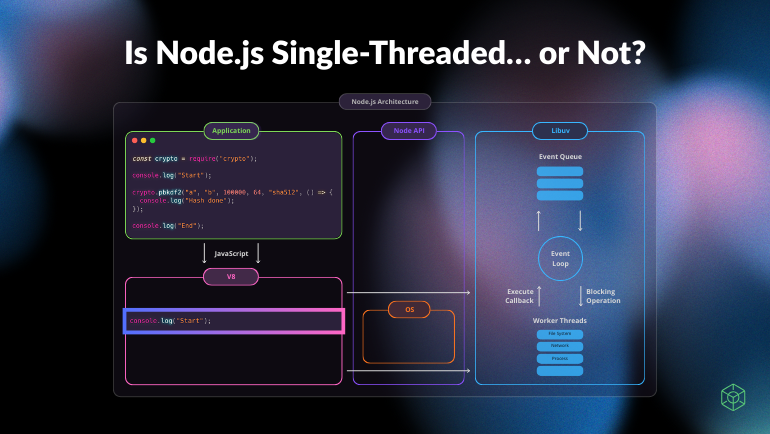
Is Node.js single-threaded? Learn how V8, libuv, the event loop, and the thread pool work together inside the Node.js runtime.
Node.js introduced a Signal requirement on HackerOne to reduce noise, improve vulnerability report quality, and support security maintainers.